Summary
As this repository is considered as Samples - (code for educational purposes), I don't think it's vital to report/submit more pieces of information to GoogleVRP regarding this repository. So I'm unveiling freely by making an issue here.
Details
I reviewed the source code of your open-source project and identified a potential security flaw in your code.
Vulnerable code link ↓
Click Here
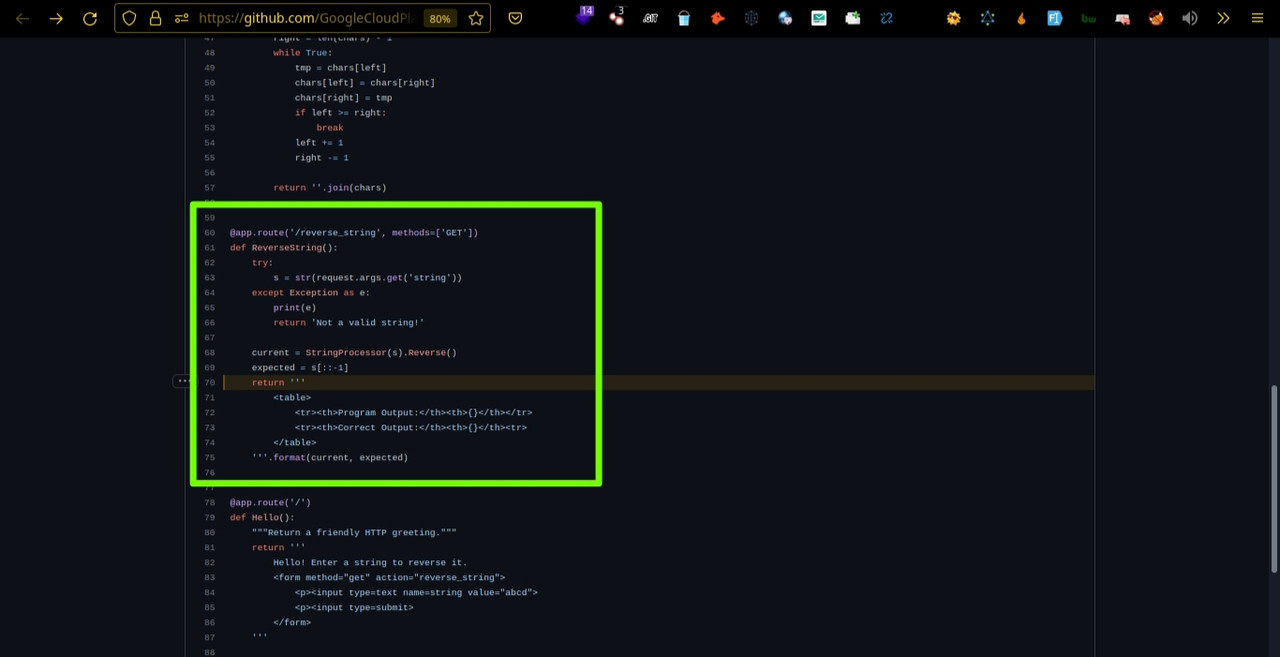
Check the code and you can see the unsanitized input from an HTTP parameter flows into the return value of ReverseString, where it is used to render an HTML page returned to the user. This allows a malicious attacker to perform Cross-Site Scripting attack (XSS) through GET request itself. The end user’s browser has no way to know that the malicious script should not be trusted, and will execute the script. Because it thinks the script came from a trusted source.
Reproduction steps ↓
1.  Run the python code (Start the service)

2.  Visit the service

3.  Use reversed XSS payloads. Eg: > >)niamod.tnemucod(trela=daolno/gvs<

4.  XSS can triggered on "/reverse_string?string=" parameter

5. Done
Proof of Concept ↓
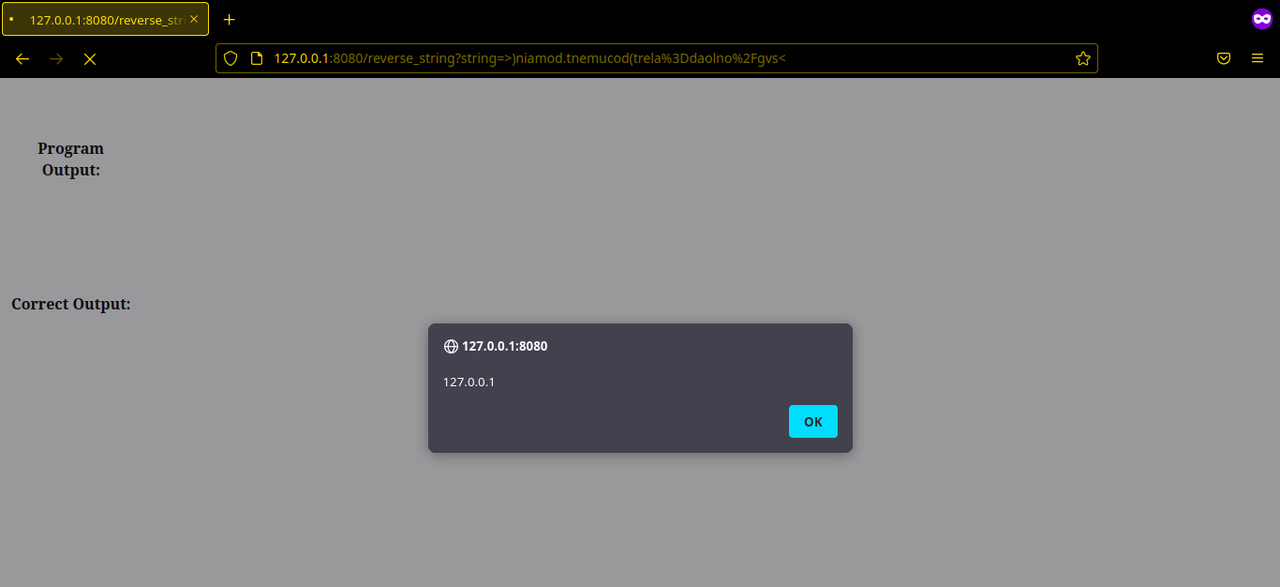
Sanitize data input in an HTTP request before reflecting it back, ensuring all data is validated, filtered or escaped before echoing anything back to the user.
I hope it helps.
Cheers,

Summary
As this repository is considered as Samples - (code for educational purposes), I don't think it's vital to report/submit more pieces of information to GoogleVRP regarding this repository. So I'm unveiling freely by making an issue here.
Details
I reviewed the source code of your open-source project and identified a potential security flaw in your code.
Vulnerable code link ↓
Click Here
Check the code and you can see the unsanitized input from an HTTP parameter flows into the return value of ReverseString, where it is used to render an HTML page returned to the user. This allows a malicious attacker to perform Cross-Site Scripting attack (XSS) through GET request itself. The end user’s browser has no way to know that the malicious script should not be trusted, and will execute the script. Because it thinks the script came from a trusted source.
Reproduction steps ↓
Proof of Concept ↓
Sanitize data input in an HTTP request before reflecting it back, ensuring all data is validated, filtered or escaped before echoing anything back to the user.
I hope it helps.
Cheers,